Privacy Exposure
Privacy exposure is a systems question: trace where identity, address, ownership, and activity become visible, searchable, reusable, or actionable before choosing a filing, address, service, or deletion path.
Start with the fact, actor, record, or remedy you need to understand, then move to the cited matrix, explainer, framework, or source record that owns that question.
For founders, property owners, and operators deciding how to evaluate a public record, ownership disclosure, address practice, privacy service, redaction route, or deletion mechanism.
Covers: visible, searchable, indexable, reusable, actionable, verified, constrained, optimized
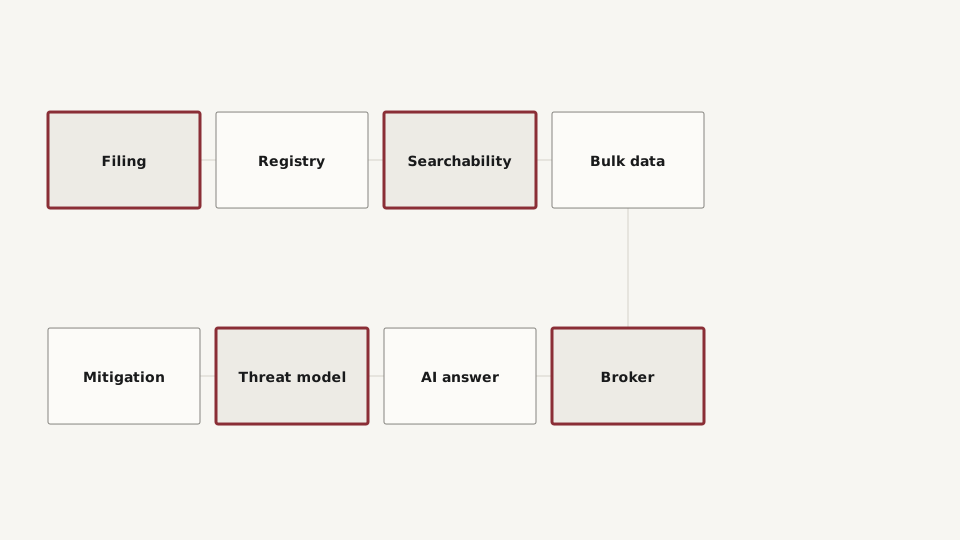
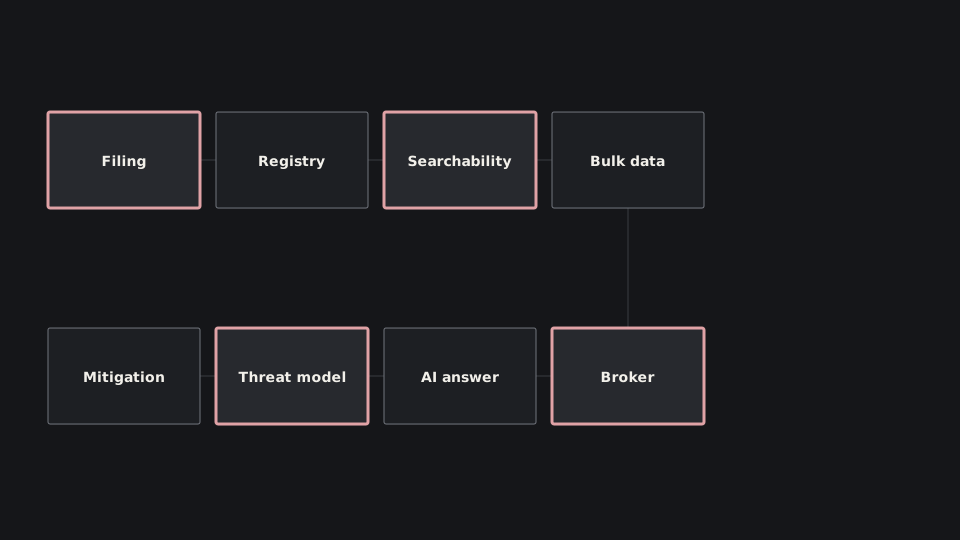
Figure 1. The Privacy hub's documented filing, searchability, reuse, data-broker and threat-model concepts placed along the exposure chain.
Source: Privacy Exposure, page description, hub thesis, Datasets and source mirrors, and Threat models and adjacent systems, /privacy-exposure/.
Start here
Choose the privacy-exposure question first
Start with the record, actor, access path, or remedy you need to understand, then use the page that owns that question instead of treating privacy as a single hidden-or-public condition.
- Address protection programs: use Address Confidentiality Programs by State for the evidence matrix and Address Confidentiality Programs by State: Evidence and Limits for the explainer.
- Ownership knowledge: use Who Still Knows the Beneficial Owner of an LLC?.
- Threat-model framing: use The Four-Layer Founder Exposure Framework.
- State comparison: use The Most Private States to Form an LLC.
- Formation-record exposure: use Anonymous LLC States.
- Mailbox and address practice: use Virtual Mailbox and CMRA Rules.
- Data-broker removal: use Get Your Business Data Deleted, State by State.
- Property-record remedies: use Property-Record Redaction by State.
Privacy-exposure research
The list below gathers this section's research pages; the pages above are the starting set for address, ownership, state-comparison, mailbox, deletion, and redaction questions.
Visible
Searchable
- Beneficial-Ownership Transparency by Jurisdiction
- Business Lifecycle Filing Exposure by State: Explainer
- Business Lifecycle Filing Exposure with Portal Access by State
- Business Lifecycle Filing Exposure With Portal Access by State: Explainer
- Business Operations Exposure
- Business Registry Searchability by State
- Does an Anonymous LLC Hide the Owner from the State?
Reusable
Constrained
Optimized
Datasets and source mirrors
Use the matrix routes for jurisdiction-level evidence and the Source Registry for the site's source-handling record.
- Address-program data: Address Confidentiality Programs by State.
- Formation-record data: Anonymous LLC States.
- Property-record remedy data: Property-Record Redaction by State.
- Ownership-disclosure data: Beneficial Ownership Transparency by Jurisdiction.
- Data-broker systems: Data Broker Registry and Deletion Mechanisms by State and Right to Delete by State.
Threat models and adjacent systems
Use the threat-model pages to separate exposure layers and mechanisms, then follow the adjacent silo that owns the underlying filing, protection, ownership-reporting, or data-broker system.
- Exposure layers: The Four-Layer Founder Exposure Framework.
- Exposure mechanics: The Five-Verb Framework.
- System separation: Private Operator Stack.
- Formation, filings, and operations: Business Systems Exposure.
- Structure and jurisdiction protection: Asset Protection Structures.
- Ownership reporting and financial-institution access: BOI & KYC Reporting.
- Registry and removal systems: Data Broker Registries & Deletion Rights.
Freshness and scope
Treat every linked page's source date, jurisdiction scope, actor scope, and notes on unknown values as controlling; this hub organizes the research and does not make stale evidence current.
Do not infer a recommendation from inclusion in this hub, and do not carry a rule, remedy, visibility condition, or deletion mechanism from one jurisdiction, record system, actor, or service into another without checking the page that owns that scope. This research is general information, not legal advice.
Datasets and mirrors
- Address Confidentiality Programs by State
- Anonymous LLC States: What Each State's Public Formation Record Actually Requires
- Property-Record Redaction by State: Eligibility, Covered Records, and Official Requests
- Beneficial-Ownership Transparency by Jurisdiction
- Data Broker Registry and Deletion Mechanisms by State
- Right to Delete by State
- Source Registry